· Prices checked · 5 min · Code audit · Humza Sheikh
Code Audit Cost: $199 to Find It, From $1,999 to Fix It
What a code audit costs at a fixed price, what it checks (security, speed, reliability), what you get back, and when an audit isn't worth paying for.
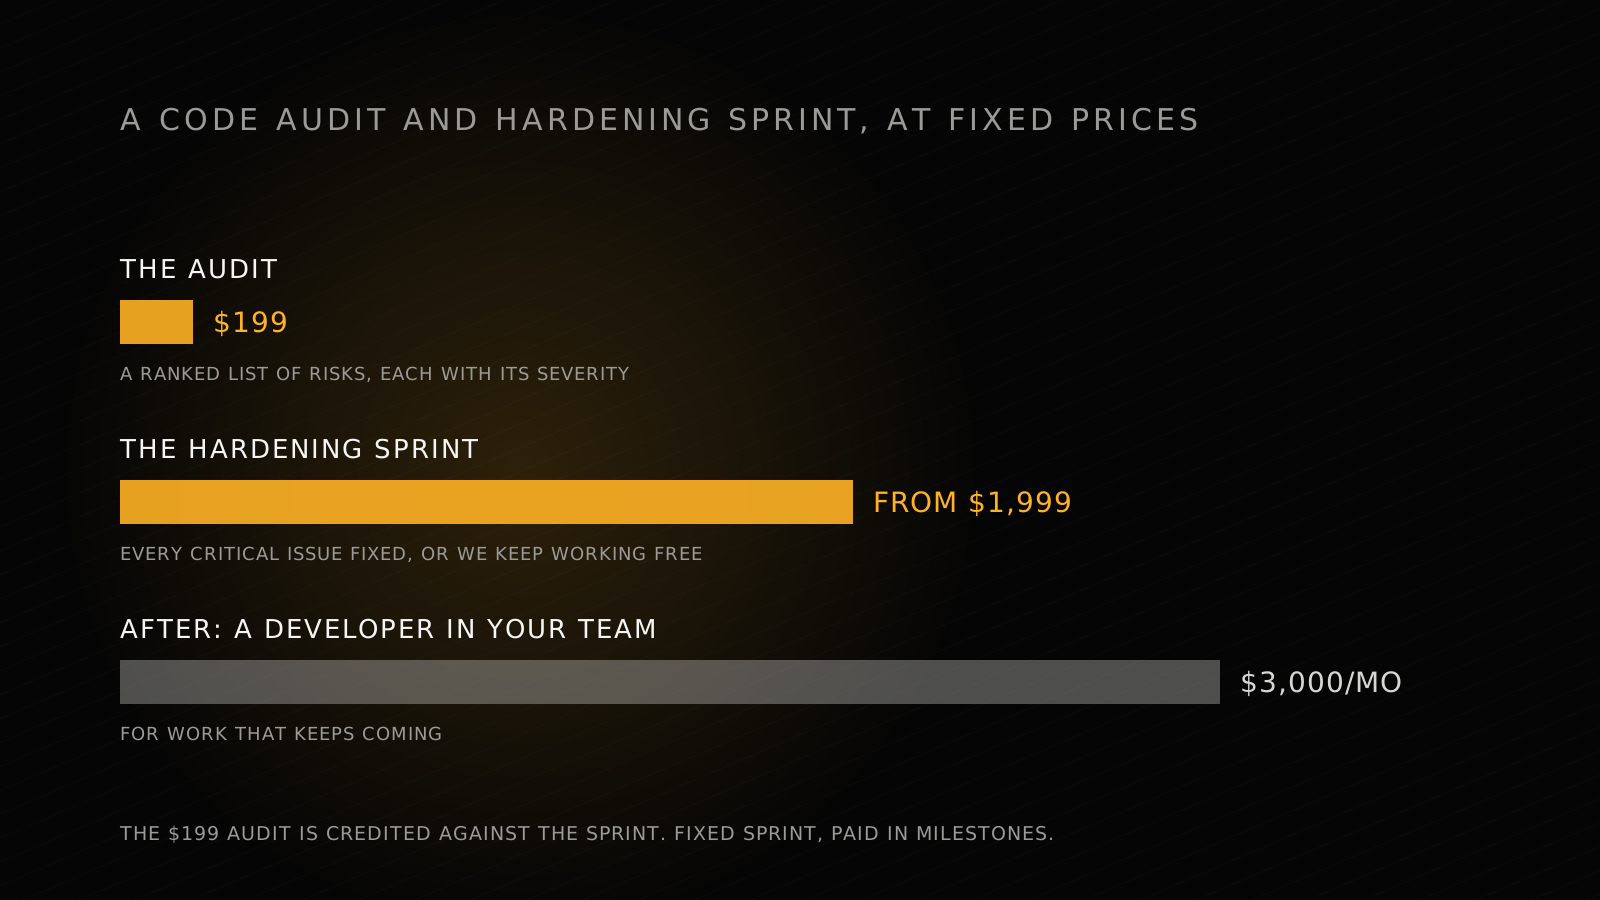
The short answer: a code audit costs $199 with us. We review your code, infrastructure and access, and you get back a ranked list of security, speed and reliability risks, each with its severity. If you want them fixed, our hardening sprint starts at $1,999, and the $199 audit is credited against it. Every critical issue the audit finds is fixed, or we keep working free until it is.
That's the whole price list, from our code audit and hardening service. Both are fixed prices, paid in milestones, so you know the cost before anyone touches the code.
How much does a code audit cost?
| What you get | Price | What it covers |
|---|---|---|
| Audit | $199 | A ranked list of security, speed and reliability risks, each with its severity |
| Hardening sprint | From $1,999 | Fixes for every critical issue the audit finds, guaranteed. The $199 audit is credited against it |
| After the sprint | A further sprint, or a developer from $3,000 a month | For work that keeps coming |
The audit stands on its own. You can stop after it, keep the list and fix the issues yourself or with your own team.
What does a code audit check?
Three areas, each of which a growing product can break on:
- Security: your code, your infrastructure and who has access to what. The things that put your data and your customers at risk.
- Speed: the slow paths your users actually feel, measured first, so the fixes go where they count.
- Reliability: monitoring and alerts, backups and recovery, and deploys you can trust, so you hear about problems before your customers do.
For the security part, a common checklist is the OWASP Top 10, which OWASP calls "a standard awareness document for developers and web application security". Its 2025 edition puts broken access control first, followed by security misconfiguration and software supply chain failures. Those three are about who can reach what, how things are set up and what you depend on, which is why we look at infrastructure and access, not only the code.
What counts as a critical issue?
Anything that risks data, payments or uptime. We agree the list with you after the audit, so "critical" is decided together before the sprint starts, not argued about afterwards. That list is what the guarantee covers: every critical issue on it is fixed, or we keep working free until it is.
Everything below critical stays on the ranked list with its severity, so you can plan it into a later sprint or hand it to your own developers.
Is a code audit worth it?
Not always. It's worth paying for when the cost of something going wrong is real:
| Worth it | Not worth it yet |
|---|---|
| You take payments or hold customer data | A throwaway prototype with no users or data |
| The product slows down as customers grow, or you find out about outages from support tickets | You're about to rewrite it from scratch anyway |
| You're about to raise, sell the business, or sign a bigger customer | Nobody will act on the list once you have it |
| A developer or agency built it and has left, and nobody knows what's in there |
If your product is still at the idea stage, spend the money on testing the idea first; we've written about what an MVP costs at a fixed price. The audit earns its price once there's something to protect.
Do you need to give access to your code?
Yes: read access for the audit, then the access the fixes need. We work in your repository and your cloud account. Fixes ship through your normal deploys, tested first and scheduled for quiet hours where needed, so your users aren't disrupted.
What does a hardened product look like afterwards?
Monitoring stays on after the sprint, so you can see the result rather than take our word for it. The same foundations run Digyfi, a storefront with more than 1 million products, serving 150K+ monthly users at 99.9% uptime. In the client's words: "Scaled us to 150K+ users with 99.9% uptime." (Zeeshan, Digyfi.) The case is on our work page.
Speed work follows the same rule of measuring first and fixing what users feel. Our PageSpeed case study shows it on this site, which went from 62 to 90+.
Common questions
How much does a code audit cost?
$199 with us, for a ranked list of security, speed and reliability risks, each with its severity. It's credited against the hardening sprint if you go ahead.
How much does it cost to fix what the audit finds?
The hardening sprint starts at $1,999, at a fixed price paid in milestones. Every critical issue the audit finds is fixed, or we keep working free until it is.
What if we need more than one sprint?
We quote the next sprint, or embed a developer in your team from $3,000 a month.
Will the fixes disrupt our users?
Fixes ship through your normal deploys, tested first and scheduled for quiet hours where needed.
Can we fix the issues ourselves?
Yes. The audit is yours for $199; the ranked list works as a plan for your own team.
Want to know what's in your code?
Start with the audit. Our code audit and hardening service gives you a ranked list for $199, then fixes every critical issue from $1,999, or we keep working free. Book a 15-minute call.
Sources
Our prices, scope, terms and guarantee are from our code audit and hardening page, 6 November 2026. The Digyfi result is from our work page. The OWASP Top 10 quote and 2025 categories are from OWASP Top 10:2025, checked 6 November 2026.